Related Topics:
Network Switch Security Best-
Australian Optical Network Switch 200G
Nokia's 1830 Photonic Service Switch (PSS) is used to upgrade Vocus' optical network between Adelaide, Brisbane and Darwin to deliver 200G with the capability to easily provide 300G and 400G in the near future. With this initiative, the Vocus capacity upgrade covers more than 7,100. The upgrade sees the addition of 200G wavelength capabilities on a more than 4100 km fiber route between Brisbane and Darwin as well as a second 3000-km route that links Adelaide, Brisbane, and Darwin. Nokia says it has supplied its 1830 Photonic Service Switch (PSS) to Vocus in support of an. A Complete Guide to FS N8510-24CD8D: A Future-Ready 200G Data Center Switch GeorgeAug 04, 20251 min read In today's rapidly evolving data center landscape, the demand for higher bandwidth, scalability, and low-latency networking has never been greater. 2T optical module solutions with 200G/lane serial electrical interfaces, which will be needed to support next generation 102. 4T switches and large-scale AI clusters.
[PDF Version]
-
Huawei Network Switch Optical Port Configuration
To enable a port on a Huawei switch, start by accessing the device's command-line interface (CLI) via a console cable or SSH. Use the system-view command to enter configuration mode, then navigate to the target port using interface GigabitEthernet 0/0/1 (replace. This section describes how to configure attributes for an optical interface. The interface split function allows a high-bandwidth physical interface on the device to be configured as multiple independent low-bandwidth interfaces. Whether you're setting up a new network segment or troubleshooting connectivity issues, understanding how to enable ports properly ensures seamless data flow while maintaining security. Single-mode/multimode fibers and. Do you have a question about the OptiX OSN 7500 and is the answer not in the manual? Page 1 HUAWEI OptiX OSN 7500 Intelligent Optical Switching System Technical Manual System Description V100R001 Huawei Technologies Proprietary. Enabling Telnet Service and Granting Access on.
[PDF Version]
-
Essential Network Security Equipment
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. Unlike firewalls, which prevent access, IDS works by detecting and alerting administrators to potential security incidents. They help to. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. ManageEngine Vulnerability Manager Plus Best for vulnerability and patch management in Windows environments 2.
-
Does the core switch have network ports
Typically, core switches are Layer 3 switches equipped with robust network management capabilities. They are characterized by numerous ports and high bandwidth, offering greater reliability, redundancy, throughput, and lower latency compared to access and aggregation switches. The devices like high-capacity transmitters are placed in this layer. The number of conventional switch ports is generally 24-48. Most of the network ports are Gigabit Ethernet or 100M Ethernet ports. Configure VLAN simple routing protocol and some simple SNMP functions. It's designed to handle significant amounts of traffic with advanced features like redundancy and scalability.
-
PAM4 Optical Network Switch Test Report
PAM4 (4-level pulse amplitude modulation) is being adopted in many applications at data rates of 50 Gb/s and higher. By encoding two bits in each symbol, PAM4 signals use half the bandwidth of t.
-
How many megabits does a 40-port fiber optic network switch have
The hardware includes 100 megabit/gigabit / 10-gigabit rate ports, electrical/optical/ PoE port, port number, MAC address table depth, forwarding delay, cache size, VLAN, isolation, etc. VERSITRON manufactures a wide range of fiber optic switches that provide links for your 10Base, 100Base, 1000Base Gigabit, and 10 Gigabit networks simultaneously. Various port sizes are available ranging from 4 up to 52 ports. It is essential for high-speed networking, offering extended reach and bandwidth capabilities. These switches play a central role in building robust, modern. In computer networking, Gigabit Ethernet (GbE or 1 GigE) is the transmission of Ethernet frames at a rate of a gigabit per second. The most popular variant, 1000BASE-T, is defined by the IEEE 802. It came into use in 1999 and has replaced Fast Ethernet in wired local networks due to. The new Cisco Nexus 9000 Series provides high 1-, 10-, 40-, and (future) 100-Gbps Ethernet densities with outstanding performance and a comprehensive feature set.
[PDF Version]
-
The core switch allows network segments to access the internet
A core switch operates at the italic core layer italic of a hierarchical network design, typically handling a massive volume of data traffic. Its primary function is to rapidly forward data packets between different aggregation switches and, ultimately, to the internet. Simply put, it's the kingpin that keeps your network humming. You may also want to know: Can a Nintendo Switch Play DS Games? ·. The layer 2 switches collect the data from core switches, identify the type of data packet and the address of the access device. Sitting at the top of the hierarchical model, core switches interconnect distribution layer switches and provide high-speed data transfer across. A core switch is a high-capacity network switch that functions as a network's backbone or core layer. This is essential for businesses, data centers, and ISPs that need fast, reliable connectivity.
[PDF Version]
-
Does a switch need an IP address to connect to a local area network
Explanation: A switch, as a Layer 2 device, does not need an IP address to transmit frames to attached devices. The IP address must be applied to a virtual interface rather than to a. In this tutorial, we'll teach you how to set up a local area network with a switch without an internet connection. A local area network is an excellent option for sharing files and resources between multiple devices, such as computers, printers, and storage devices. Using a switch, you can create a. Not every switch or AP comes equipped with an IP address: Unmanaged Switches: These basic switches operate without configuration interfaces and do not possess IP addresses. They work transparently, forwarding data without any need for IP identification. However, when a switch is accessed remotely through the network, it must have a Layer 3 address.
[PDF Version]
-
Network Gateway Core Switch
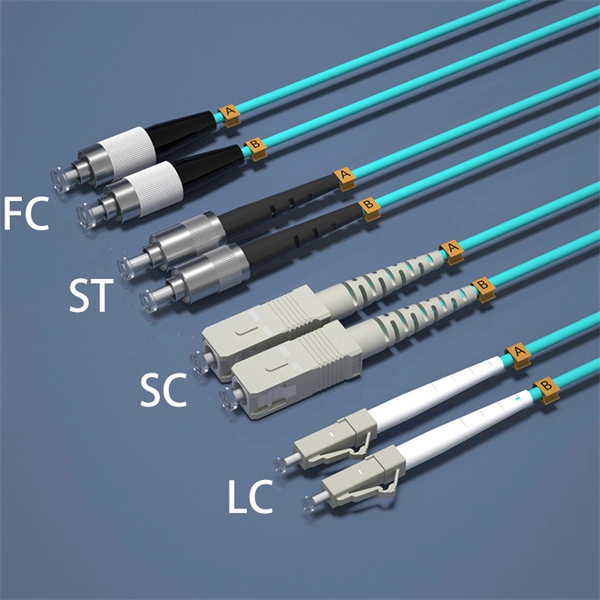
Includes dual power supplies, hot-swappable modules, link aggregation (LAG), and support for HSRP/VRRP. Modular chassis or stackable designs make it easy to scale as your network grows. Engineered to aggregate massive volumes of data from distribution switches, it provides ultra-low latency and maximum throughput to ensure uninterrupted routing and packet. The hierarchy Ethernet network is a three-layer integrated setup of networking devices. These networks are designed with three tiers that facilitate strategic installation, management, and maintenance, and so on. 0/24 you assign an SVI to every layer-2 switch and give it an IP in this range and the gateway for all the SVIs should be on the core (172. 1/24 example: access switch-1 172. 13/24. Network planning 1: The AR router accesses the Internet through DHCP or PPPoE on the WAN interface or the static IP address allocated by the carrier.
[PDF Version]
-
Network security device management interface
Cisco's Adaptive Security Device Manager (ASDM) is a web-based tool designed to manage network security devices from a central location. It serves as a user-friendly graphical interface for configuring, monitoring, and troubleshooting Cisco firewall appliances. Watch this demo for securing your firewall management interface, which details best practices for securing your management. The Cisco Router and Security Device Manager (SDM) is an intuitive, graphical user interface. For more information about Cisco SDM, please visit By enforcing standardized security policies and. Exposed network device management interfaces on the internet, encompassing routers, switches, and firewalls, represent critical attack vectors that demand immediate identification and stringent security measures.
[PDF Version]
-
Office Network Security Equipment Configuration Standards
For improved network security, the Trusted Computing Group (TCG) is developing standards/guidance that specifically addresses the security of networking equipment. The TCG Guidance for Securing Network Equipment Preview Synopsis provides a summary of the ongoing. Establish, implement, and actively manage (track, report on, correct) the security configuration of network infrastructure devices using a rigorous configuration management and change control process in order to prevent attackers from exploiting vulnerable services and settings. Why is this CIS. This publication has been developed by NIST in accordance with its statutory responsibilities under the Federal Information Security Modernization Act (FISMA) of 2014, 44 U. NIST is responsible for developing information security standards and. Securing network devices is essential for preventing unauthorized access and maintaining network integrity. By enforcing standardized security policies and. This article provides best practices for each of these aspects, ensuring a robust and efficient office network setup. Steps for Provisioning Servers 3.
[PDF Version]