Related Topics:
Guide Security Devices Networking-
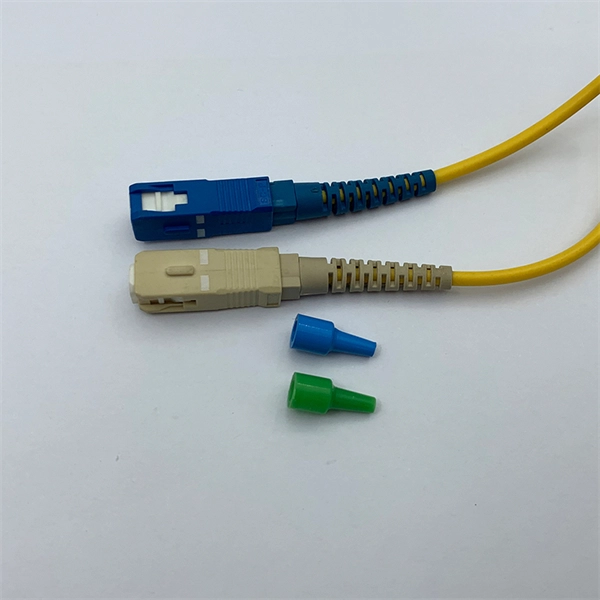
6 Major Network Security Devices
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices are designed to monitor network traffic, analyze data flow, and block harmful activities to ensure the integrity and confidentiality of. Network Security devices are typically physical or virtualized hardware appliances, with vendor specific software installed. Occasionally, businesses purchase commodity server hardware and install custom software to create their own network security device. Depending on your company's particular. Next-generation firewalls (NGFW) offer deep packet inspection, intrusion prevention, and application awareness. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. Traffic can be permitted or denied based on this address, enabling the blocking of malicious sources or botnets.
[PDF Version]
-
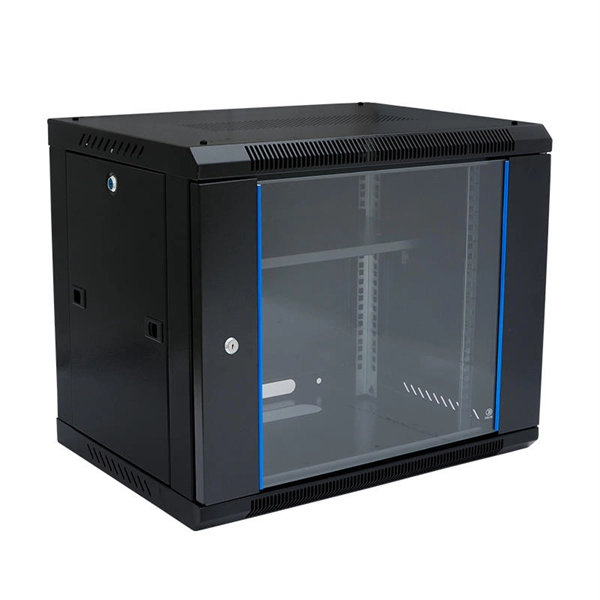
Function of the guide rail in the distribution box
Guide rails, also known as linear guides, are mechanical elements designed to ensure smooth, precise and controlled linear movement of objects. They generally consist of two main components: the rail itself and a sliding carriage that moves along the rail. The guide rail slot seat is provided with several. Busbars: These are solid strips of copper or aluminum that transfer electricity from the main source to the individual circuits inside the box. It integrates power distribution, protection, and monitoring capabilities, and is responsible for distributing power to entire commercial or residential. The distribution box (DB box) helps safely and efficiently distribute electrical power.
-
Customization Process for New Reconfigurable Optical Add-Drop Multiplexers for Security Applications
Network operators diversify service offerings and enhance network efficiency by leveraging bandwidth-variable transceivers and colorless flexible-grid reconfigurable optical add-drop multiplexers (RO.
-
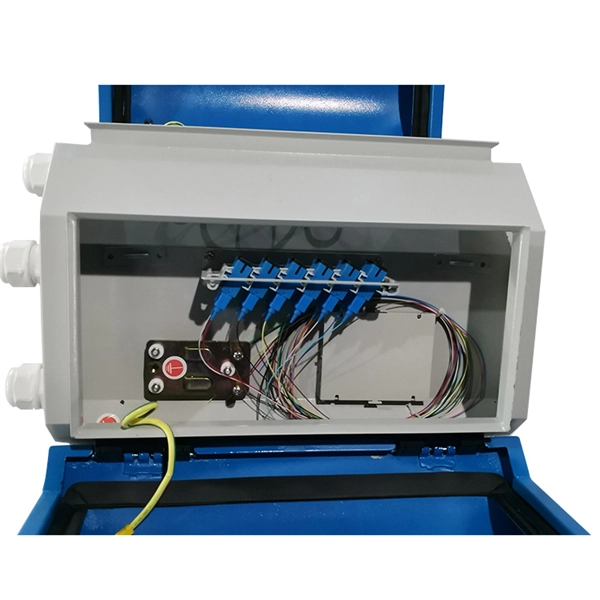
Network security device management interface
Cisco's Adaptive Security Device Manager (ASDM) is a web-based tool designed to manage network security devices from a central location. It serves as a user-friendly graphical interface for configuring, monitoring, and troubleshooting Cisco firewall appliances. Watch this demo for securing your firewall management interface, which details best practices for securing your management. The Cisco Router and Security Device Manager (SDM) is an intuitive, graphical user interface. For more information about Cisco SDM, please visit By enforcing standardized security policies and. Exposed network device management interfaces on the internet, encompassing routers, switches, and firewalls, represent critical attack vectors that demand immediate identification and stringent security measures.
[PDF Version]
-
Office Network Security Equipment Configuration Standards
For improved network security, the Trusted Computing Group (TCG) is developing standards/guidance that specifically addresses the security of networking equipment. The TCG Guidance for Securing Network Equipment Preview Synopsis provides a summary of the ongoing. Establish, implement, and actively manage (track, report on, correct) the security configuration of network infrastructure devices using a rigorous configuration management and change control process in order to prevent attackers from exploiting vulnerable services and settings. Why is this CIS. This publication has been developed by NIST in accordance with its statutory responsibilities under the Federal Information Security Modernization Act (FISMA) of 2014, 44 U. NIST is responsible for developing information security standards and. Securing network devices is essential for preventing unauthorized access and maintaining network integrity. By enforcing standardized security policies and. This article provides best practices for each of these aspects, ensuring a robust and efficient office network setup. Steps for Provisioning Servers 3.
[PDF Version]
-
Essential Network Security Equipment
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. Unlike firewalls, which prevent access, IDS works by detecting and alerting administrators to potential security incidents. They help to. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. ManageEngine Vulnerability Manager Plus Best for vulnerability and patch management in Windows environments 2.
-
Does a switch have a maximum number of connected devices
The network switch may include ports for 5, 8, 12, 16, 24 or 28 devices, whereas corporate ethernet switches may commonly offer between 32 and 128 connections. Each device connected to a port on the switch will typically have access to the full bandwidth available on that port. Can a switch connect multiple devices? Switches are key building blocks for any network. ) to two PCs, such that you can choose to control the whole setup from either one of those PCs. My first thought was to get a 10-port USB 3. When you have separate vlans you need routed interfaces to route traffic between them.
-
When relay protection devices are in operation
A protective relay operates by continuously monitoring electrical parameters, detecting abnormalities, making decisions, and triggering circuit breakers to isolate faulty sections. This process helps protect equipment, maintain power system stability, and ensure safety for. Protective relays and devices have been developed over 100 years ago to provide “lastline”of defense for the electrical systems. They are intended to quickly identify a fault and isolate it so the balance of the system continue to run under normal conditions. : 4 The first. Relion protection and control relays for several application reduce complexity.
-
Passive internal optical devices
Passive optical components are devices that perform their function without requiring external power or active control. They are the fundamental pipes of a PIC, responsible for manipulating the flow of light through processes such as guiding, splitting, combining, filtering, and. Passive vs. Passive. ction (optical isolators). The coverage includes theoretical aspects, prac-tical implementations, standardisation issues, and typical characteristics of fib es and fibre-optic cables. They don't add gain or require power, but they decide how efficiently, cleanly, and safely light moves through your network or laser chain. This guide blends clear definitions with engineer-grade selection criteria, with a. The devices can be categorized as either passive or active components. Just as a filter in a coffee pot or a sprayer head in a.
[PDF Version]
-
Four common passive optical devices are
Some of the most common optical passive components include optical couplers, optical splitters, optical filters, optical connectors, optical attenuators, optical circulators, optical isolators, optical switches, and optical add/drop multiplexers. The treatment of optical isolators includes their fundamental principles, polarisation-independent, and planar. Optics engineering focuses on transmitting data using light, a method providing the high speeds and vast bandwidth necessary for modern digital life. Passive optical components play a fundamental role within this infrastructure. They don't add gain or require power, but they decide how efficiently, cleanly, and safely light moves through your network or laser chain. This guide blends clear definitions with engineer-grade selection criteria, with a.
[PDF Version]
-
Canadian Active Optical Devices QSFP-DD
QSFP-DD is a new module and cage/connector system similar to current QSFP, but with an additional row of contacts providing for an eight lane electrical interface. It is being developed by the QSFP-DD MSA as a key part of the industry's effort to enable high-speed solutions. It is designed for relatively short connection, offering high-density solution alternative for system providers. Our active optical cable assembly portfolio provides improved cable flexibility and longer reach as compared to both traditional passive copper and emerging active copper (ACC/AEC) solutions, supporting high performance computing, data center and networking interconnect applications. TE. Smartoptics QSFP-DD transceivers provide cost-efficient 400G and 800G optical networking. 3bs Annex 120E over operating case temperature 0 de voltage generated by the host. Specification include ff cts of ground FP DD MSA Har cu tomization can be.
[PDF Version]