Related Topics:
Managed Security Services Secmentis-
Venezuela Export of 50kW Off-Grid Power System CIF Price
The electricity sector in Venezuela is heavily dependent on hydroelectricity, which accounted for 64% of the nation's electricity generation in 2021. Besides hydroelectric power, Venezuela also relies on and, contributing 25% and 11%, respectively, to the total electricity output that year. The country operates six hydroelectric plants, totaling a capacity of 16,010 megawatts (MW), with the Central Hidroeléctrica Guri in being the most significant, accounting for 64% of Venezuela's hydroelect.
-
Managed switch as aggregation layer
As the aggregation point of access switches, the aggregation switch is required with the ability to process the access layer information and submits it to the upstream chain of the core layer. And it needs the function of network isolation and segmentation as well. 5G, and 10G speeds for flexible customization, ensuring optimal performance, compatibility, and scalability Flexible interface options like copper, fiber, and PoE ensure seamless integration and cost-effective deployment Supports stacking for easier management, improved redundancy. The aggregation (sometimes also called distribution) layer is a real crossroad. Its primary goal is to increase network scalability by providing a single place to interconnect multiple access switches and the core layer.
-
Managed Intelligent PDU Header
Intelligent PDU with CAN bus interface for use with CMC III or PDU managed, switch function and energy data logging per output. Input with CEE connector (16 A/32 A), with BS 1363 (UK) outputs. Managing and installing a rack power distribution unit (PDU) has never been easier than with the EL2P PDU. Remote power control, real-time energy metering, SNMP/Modbus integration. Products include advanced solutions for real-world power, environmental, and security management problems in. See why the world's leading companies trust Raritan's PX PDUs to deliver reliable power to critical devices. It inherits the innovative fully modular design from the classic MPDU family. Switched PDU models are also available that can provide remote on/off outlet switching functionality from anywhere in the world.
[PDF Version]
-
Office Network Security Equipment Configuration Standards
For improved network security, the Trusted Computing Group (TCG) is developing standards/guidance that specifically addresses the security of networking equipment. The TCG Guidance for Securing Network Equipment Preview Synopsis provides a summary of the ongoing. Establish, implement, and actively manage (track, report on, correct) the security configuration of network infrastructure devices using a rigorous configuration management and change control process in order to prevent attackers from exploiting vulnerable services and settings. Why is this CIS. This publication has been developed by NIST in accordance with its statutory responsibilities under the Federal Information Security Modernization Act (FISMA) of 2014, 44 U. NIST is responsible for developing information security standards and. Securing network devices is essential for preventing unauthorized access and maintaining network integrity. By enforcing standardized security policies and. This article provides best practices for each of these aspects, ensuring a robust and efficient office network setup. Steps for Provisioning Servers 3.
[PDF Version]
-
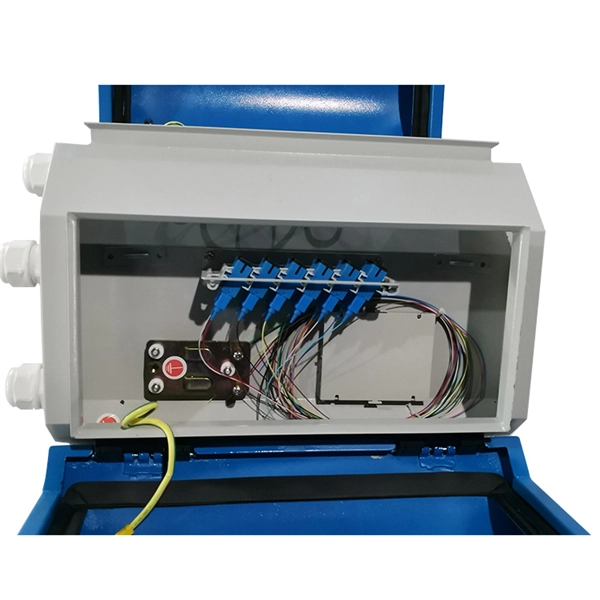
Network security device management interface
Cisco's Adaptive Security Device Manager (ASDM) is a web-based tool designed to manage network security devices from a central location. It serves as a user-friendly graphical interface for configuring, monitoring, and troubleshooting Cisco firewall appliances. Watch this demo for securing your firewall management interface, which details best practices for securing your management. The Cisco Router and Security Device Manager (SDM) is an intuitive, graphical user interface. For more information about Cisco SDM, please visit By enforcing standardized security policies and. Exposed network device management interfaces on the internet, encompassing routers, switches, and firewalls, represent critical attack vectors that demand immediate identification and stringent security measures.
[PDF Version]
-
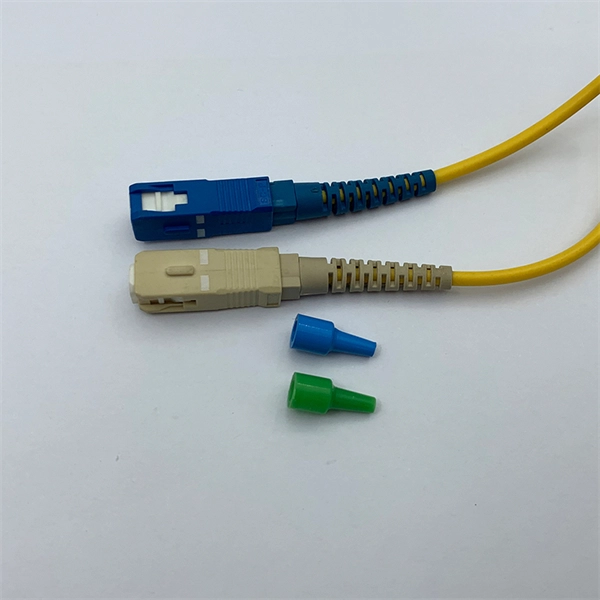
6 Major Network Security Devices
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. These devices are designed to monitor network traffic, analyze data flow, and block harmful activities to ensure the integrity and confidentiality of. Network Security devices are typically physical or virtualized hardware appliances, with vendor specific software installed. Occasionally, businesses purchase commodity server hardware and install custom software to create their own network security device. Depending on your company's particular. Next-generation firewalls (NGFW) offer deep packet inspection, intrusion prevention, and application awareness. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. Traffic can be permitted or denied based on this address, enabling the blocking of malicious sources or botnets.
[PDF Version]