Related Topics:
Mx68 Cloud Managed Security-
Essential Network Security Equipment
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. Unlike firewalls, which prevent access, IDS works by detecting and alerting administrators to potential security incidents. They help to. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. ManageEngine Vulnerability Manager Plus Best for vulnerability and patch management in Windows environments 2.
-
Office Network Security Equipment Configuration Standards
For improved network security, the Trusted Computing Group (TCG) is developing standards/guidance that specifically addresses the security of networking equipment. The TCG Guidance for Securing Network Equipment Preview Synopsis provides a summary of the ongoing. Establish, implement, and actively manage (track, report on, correct) the security configuration of network infrastructure devices using a rigorous configuration management and change control process in order to prevent attackers from exploiting vulnerable services and settings. Why is this CIS. This publication has been developed by NIST in accordance with its statutory responsibilities under the Federal Information Security Modernization Act (FISMA) of 2014, 44 U. NIST is responsible for developing information security standards and. Securing network devices is essential for preventing unauthorized access and maintaining network integrity. By enforcing standardized security policies and. This article provides best practices for each of these aspects, ensuring a robust and efficient office network setup. Steps for Provisioning Servers 3.
[PDF Version]
-
Use network security equipment correctly and effectively
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Build a vulnerability management program. We'll explore how powerful solutions, like those from industry leaders Cisco and Meraki, can help you build secure, seamless. This guide provides a detailed roundup of the most critical network security best practices for modern enterprises.
-
Managed Intelligent PDU Header
Intelligent PDU with CAN bus interface for use with CMC III or PDU managed, switch function and energy data logging per output. Input with CEE connector (16 A/32 A), with BS 1363 (UK) outputs. Managing and installing a rack power distribution unit (PDU) has never been easier than with the EL2P PDU. Remote power control, real-time energy metering, SNMP/Modbus integration. Products include advanced solutions for real-world power, environmental, and security management problems in. See why the world's leading companies trust Raritan's PX PDUs to deliver reliable power to critical devices. It inherits the innovative fully modular design from the classic MPDU family. Switched PDU models are also available that can provide remote on/off outlet switching functionality from anywhere in the world.
[PDF Version]
-
Managed switch as aggregation layer
As the aggregation point of access switches, the aggregation switch is required with the ability to process the access layer information and submits it to the upstream chain of the core layer. And it needs the function of network isolation and segmentation as well. 5G, and 10G speeds for flexible customization, ensuring optimal performance, compatibility, and scalability Flexible interface options like copper, fiber, and PoE ensure seamless integration and cost-effective deployment Supports stacking for easier management, improved redundancy. The aggregation (sometimes also called distribution) layer is a real crossroad. Its primary goal is to increase network scalability by providing a single place to interconnect multiple access switches and the core layer.
-
Cloud Computing Application-Level EDFAEML Selection Guide
The Microsoft Cloud Adoption Framework for Azure is a full lifecycle framework that enables cloud architects, IT professionals, and business decision makers to achieve their cloud adoption goals. It provides be.
-
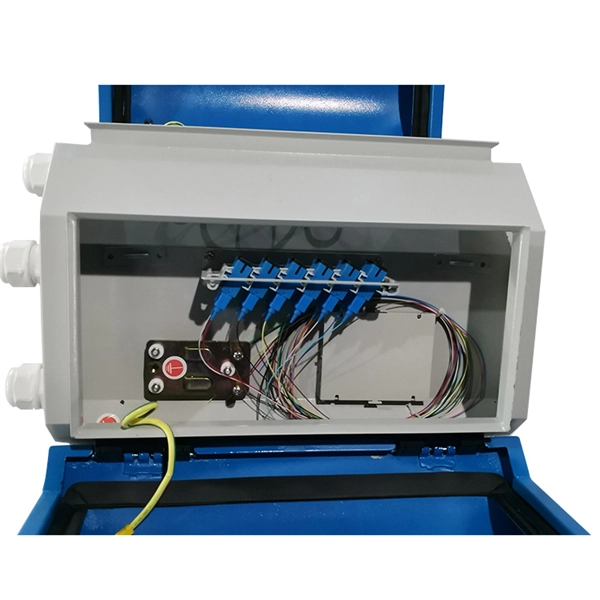
Network security device management interface
Cisco's Adaptive Security Device Manager (ASDM) is a web-based tool designed to manage network security devices from a central location. It serves as a user-friendly graphical interface for configuring, monitoring, and troubleshooting Cisco firewall appliances. Watch this demo for securing your firewall management interface, which details best practices for securing your management. The Cisco Router and Security Device Manager (SDM) is an intuitive, graphical user interface. For more information about Cisco SDM, please visit By enforcing standardized security policies and. Exposed network device management interfaces on the internet, encompassing routers, switches, and firewalls, represent critical attack vectors that demand immediate identification and stringent security measures.
[PDF Version]