Related Topics:
Cs86 20xs4vs2qxs Port 1025ge-
Port down after VLAN segmentation on access layer switch
Symptom: The switchport is shutting down or not passing traffic after connecting a device. Cause: Port security may be misconfigured, leading to violations that cause the port to go into an error-disabled state. Please rate and mark as an accepted solution if you have found any of the information provided useful. This then could assist others on these forums to find a valuable answer and broadens the. An SVI stuck in up/down means something is wrong with the underlying VLAN — no active ports, a deleted VLAN, or STP blocking every path. Here is how to diagnose and fix every cause. You configure an SVI, assign an IP address, type no shutdown, and expect it to come up. Instead, show ip interface. Network segmentation is crucial for security, performance, and efficient network management., computers, printers) connect to a switch.
[PDF Version]
-
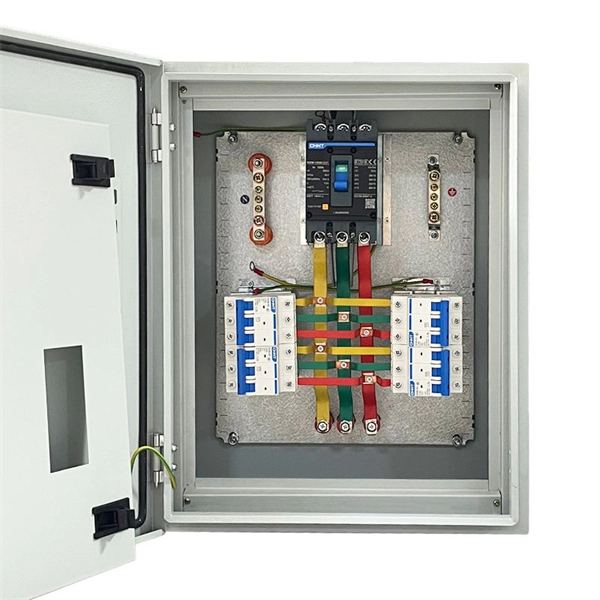
20 000 watt distribution box
The distribution cabinet has a 20kW power capacity, with 6 output circuits of AC 220V and a 63A main circuit breaker. It operates at 380V ±15%, 50Hz input, featuring overvoltage, surge, short circuit, overcurrent, overload, and leakage protection. Wieland is your experienced and reliable partner for efficient, pluggable and decentralized electrical installation. By manufacturing essential parts internally, we eliminate reliance on third-party distribution box suppliers, saving on markups and. The distribution boxes from the Power series are specially designed for the larger distributions, suitable for applications in challenging environments. The POWERBOX (left) is a single housing that can be cleverly combined in order to obtain the desired size of the distribution unit. Control methods include manual (button/knob) and. The PLC intelligent power distribution box is equipped with PLC as the interlligent control unit along with monitoring sensors to reslize the external environment monitoring and real- time control of abnormal conditions. it can work compatibly with electronic computers for remote.
[PDF Version]
-
CFP SFP for Railway Communication
The CFP transceiver is specified by a multi-source agreement (MSA) among competing manufacturers. The CFP was designed after the Small Form-factor Pluggable transceiver (SFP) interface, but is significantly larger to support 100 Gbit/s. While the electrical connection of a CFP uses 10 × 10 Gbit/s lanes in each direction (RX, TX), the optical connection can support both 10 × 10 Gbit/s and. OverviewThe C form-factor pluggable (CFP, 100G form factor pluggable, where C is : "hundred") is a CFP transceivers can support a single 100 Gbit/s signal like or or one or more 40 Gbit/s signals like 40GbE,, or /. The in 2016 published t. The original CFP specification was proposed at a time when 10 Gbit/s signals were far more achievable than 25 Gbit/s signals. As such to achieve 100 Gbit/s line rate, the most affordable solution was based on 1.
[PDF Version]
-
Can an SFP connect to an SPF optical module
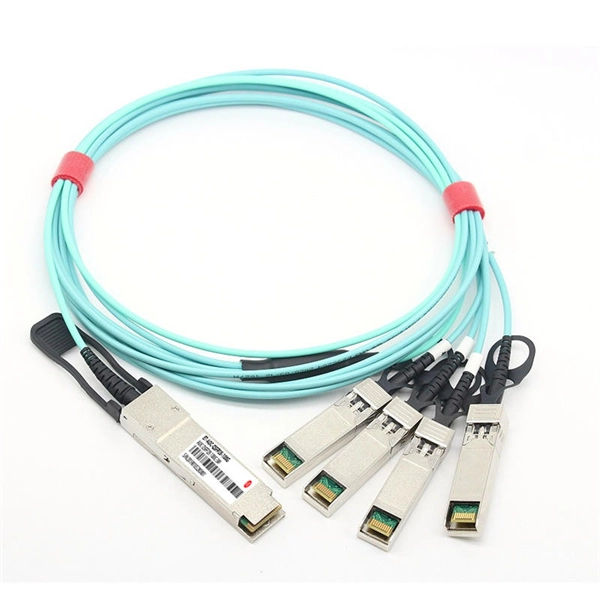
In simple terms, if an SFP module fits the port, connects properly, and enables the device to function as expected, it can be considered compatible. The compatibility between SFP vs SFP+ largely depends on the port and module combination. The. Small Form-factor Pluggable (SFP) is a compact, hot-pluggable network interface module format used for both telecommunication and data communications applications. An SFP interface on networking hardware is a modular slot for a media-specific transceiver, such as for a fiber-optic cable or a copper. The short answer is yes, you can connect an SFP module on one end of your fiber link and an SFP+ on the other end. However, the following conditions must be met for this configuration to work: 1. Speed negotiation – The SFP+ module needs to be dual-rate to operate at the same speed as the SFP. The SFP+ port is a high-speed optical-to-optical signal conversion port, mainly used for 10G Ethernet and Fiber Channel network applications.
[PDF Version]
-
Fiber optic leased line connected to a Layer 3 switch
A leased line is not a long physical cable extended to two or more locations as others perceived. It uses a specialized switching device that acts as a signal booster to make the connection a point-to-point li.
-
Selection of Monitoring Access Layer Switches
When choosing access layer switches, there are many points to consider, such as port density, port speed, security, scalability, deployment and management methods, as well as cost. Port density refers to the number of ports available on a single. Access layer switches sit at the edge of a LAN and connect computers, printers, phones, and IoT gadgets to the wider network. This white paper introduces the following three types of network switches and further discusses the selection criteria for each switch. The hierarchy Ethernet network. As the physical entity of the access layer, access switches are responsible for connecting both to the distribution layer switches and to the end devices as well as ensuring the packets are delivered to the end devices.
[PDF Version]
-
Cisco Access Layer Switch Permissions
Cisco IOS devices use privilege levels for more granular security and Role-Based Access Control (RBAC) in addition to usernames and passwords. To access Cisco Feature Navigator, go to http://www. By default: Each command in IOS is assigned a default. We can configure different command access based on priviledge level of user logged in. Level 15. In this guide, we'll break down everything you need to know about Cisco ACLs: from the basics of standard and extended lists, to advanced configuration examples, to real-world troubleshooting tips that save hours of downtime. If the startup configuration has a convoluted type 9 secret, and you downgrade to a release prior to Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device.
-
Layer 2 switch cannot ping aggregation layer
The show interfaces terse command shows that the LAG is down. Verify that all member ports are up. You must be in the global configuration context: switch (config)#. While creating the layer 2 aggregate interface, the system automatically creates a layer 2 static aggregation group numbered the same. This command does not impact the administrative. The gateways of both L2 switches is the same You can ping the firewall, L3 and L2-SW2 from L2-SW1 You can ping the L2-SW1 from the L3 switches You can't ping the L2-SW1 from the firewall; The config on both L2 switches is the same apart from the below which is in the config for the switch i cant. Static LAG or LACP does not link up or aggregate the speed. When LACP (Link Aggregation Control Protocol) or static LAG (Link Aggregation Group) is not functioning properly, common troubleshooting steps and checkpoints include: 1.
[PDF Version]
-
Access Layer Switch VLAN and MAC Binding
The MAC-based VLAN feature allows incoming untagged packets to be assigned to a VLAN and in that way, you can classify traffic based on the source MAC address of the packet. You can use VLAN maps to filter traffic between devices in the same VLAN. Unsupported protocols are. VLANs can be assigned based on interfaces, MAC addresses, IP subnets, protocols, and policies (MAC addresses, IP addresses, and interfaces). Table 5-2 compares different VLAN assignment modes. A network administrator preconfigures a PVID for each interface on. In this article, we will dive into switching basics, focusing specifically on VLANs (Virtual Local Area Networks) and MAC address tables, two critical components in managing traffic within local networks. It is required that Laptop A can only access Server A and Laptop B can only access Server B, no matter which meeting room the laptops are being used in. VLAN access-map configuration is very similar to the Route-map configuration.
[PDF Version]
-
H3C2 Layer Aggregation Switch
Ethernet link aggregation bundles multiplephysical Ethernet links into one logical link, called an aggregate link. Linkaggregation has the following benefits: · Increased bandwidth beyond the limits of anysin.
-
What layer switch is the core switch
A core switch is a high-capacity, high-performance Layer 3 switch positioned at the physical backbone of an enterprise network. The primary transmission and routing of data signals take place at the core layer only. The devices like high-capacity transmitters are placed in this. A core switch is the backbone of a large-scale network, designed to handle massive volumes of traffic with ultra-low latency and maximum reliability. Usually, complex network systems at the offices and data centers utilize the core switch to divide the traffic. In these switches, the data routed and switched.
-
Configure a Layer 3 Core Switch
To start using layer 3 routing, navigate to the Switching > Configure > Routing & DHCP page. You can configure a port as a Layer 2 interface or a Layer 3 interface. A routed interface is a physical port that. UPDATED: 2020 – Cisco Catalyst switches equipped with the Enhanced Multilayer Image (EMI) can work as Layer 3 devices with full routing capabilities. On a Layer3-capable switch, the port interfaces work as. This article outlines a basic example of how layer 3 routing functionality on MS series switches could be implemented. Sign in with your Cisco SSO or create a free account to start. Layer 3 interfaces are used to forward IPv4 and IPv6 packets using static or dynamic routing protocols. This example uses router configurations of AR3600 V200R007C00SPCc00.
[PDF Version]
-
Front-end access layer switch
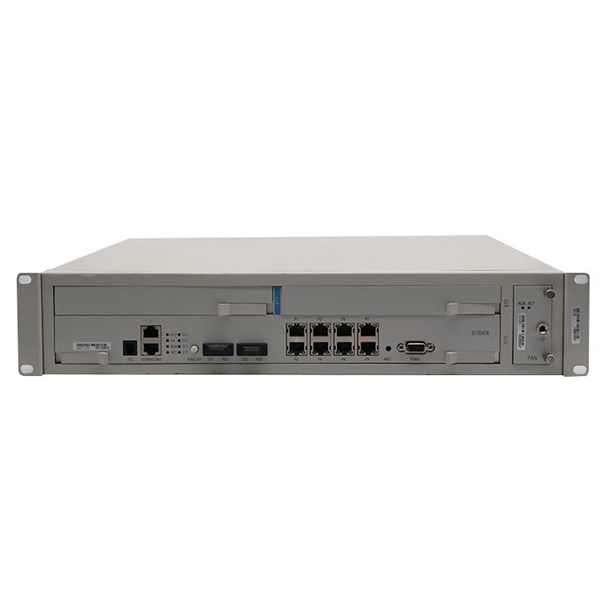
Access Layer Switches: Operating at the network's edge, access switches connect end-user devices like PCs, printers, IP phones, and wireless access points. They are characterized by high port density, cost-effectiveness, security features at the edge, and often PoE support. The access layer is where endpoints (such as phones, laptops, video-conferencing sets, printers, IoT sensors, IP cameras, and servers) are primarily connecting to the network. Wireless access points are also connected here and provide further access.
-
Is Convergence a Layer 3 switch
It is also known as the Top-of-Rack (ToR) switch. A three-tier architecture is illustrated as follows. This document provides design guidance for implementing a routed (Layer 3 switched) access layer using EIGRP or OSPF as the campus routing protocol. What's a Layer 1 (L1) Switch? Let's be real—“L1 switch” is kind of a misnomer. It works in our network by simply allowing connected devices that are on the same subnet or virtual LAN (VLAN) to exchange information at lightning speed, just like a switch. Aggregation Layer: This layer connects to the access switches and also provides other services (FW, SLB, etc.