Related Topics:
Roles Permissions Security Azure-
Cisco Access Layer Switch Permissions
Cisco IOS devices use privilege levels for more granular security and Role-Based Access Control (RBAC) in addition to usernames and passwords. To access Cisco Feature Navigator, go to http://www. By default: Each command in IOS is assigned a default. We can configure different command access based on priviledge level of user logged in. Level 15. In this guide, we'll break down everything you need to know about Cisco ACLs: from the basics of standard and extended lists, to advanced configuration examples, to real-world troubleshooting tips that save hours of downtime. If the startup configuration has a convoluted type 9 secret, and you downgrade to a release prior to Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device.
-
Use network security equipment correctly and effectively
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Build a vulnerability management program. We'll explore how powerful solutions, like those from industry leaders Cisco and Meraki, can help you build secure, seamless. This guide provides a detailed roundup of the most critical network security best practices for modern enterprises.
-
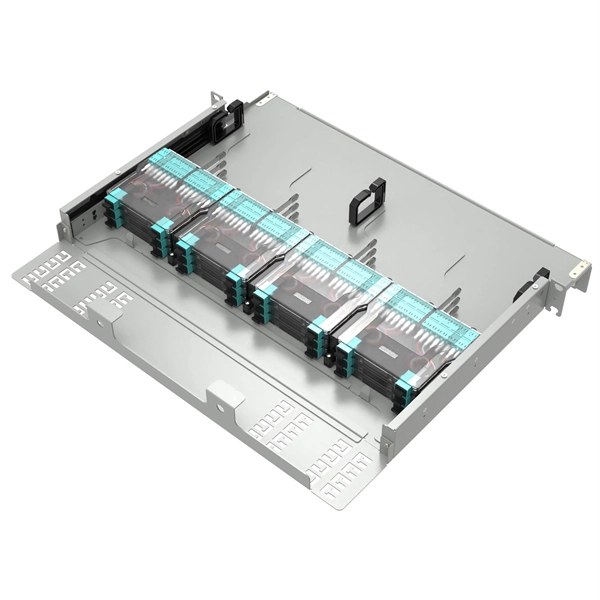
How to monitor fiber optic patch cord attenuation
Three methods exist for measuring it: cutback (the reference standard), insertion loss (the field standard), and OTDR (the diagnostic tool). This guide walks through all three. Each has different accuracy, equipment needs, and use cases. This note also provides background information on system link configurations, test equipment and system component considerations that influence. Optical Signal Attenuation is the single greatest factor limiting the distance and performance of your network. Understanding it is crucial for anyone involved in data centers, telecommunications, or enterprise networking. This guide will demystify signal loss, explore its causes, and show you how. Testing fiber optic components and cable plants requires making several measurements with the most common measurement parameters listed in the Table below. Optical power, required for measuring source power, receiver power and, when used with a test source, loss or attenuation, is the most. Fiber optic signal loss, also known as attenuation, occurs when optical signals weaken as they travel through the fiber.
[PDF Version]
-
Essential Network Security Equipment
Network security devices are hardware or virtual appliances designed to protect computer networks from unauthorized access, data breaches, and cyberattacks. Unlike firewalls, which prevent access, IDS works by detecting and alerting administrators to potential security incidents. They help to. Networking devices play a crucial role in cybersecurity, ensuring secure communication, traffic filtering, and threat prevention. ManageEngine Vulnerability Manager Plus Best for vulnerability and patch management in Windows environments 2.
-
Network security device management interface
Cisco's Adaptive Security Device Manager (ASDM) is a web-based tool designed to manage network security devices from a central location. It serves as a user-friendly graphical interface for configuring, monitoring, and troubleshooting Cisco firewall appliances. Watch this demo for securing your firewall management interface, which details best practices for securing your management. The Cisco Router and Security Device Manager (SDM) is an intuitive, graphical user interface. For more information about Cisco SDM, please visit By enforcing standardized security policies and. Exposed network device management interfaces on the internet, encompassing routers, switches, and firewalls, represent critical attack vectors that demand immediate identification and stringent security measures.
[PDF Version]
-
How to monitor optical switch links
Execute the following command to view detailed interface and optical module status: show interface <interface-type> <interface-number>Execute the following command to view detailed interface and optical module status: show interface <interface-type> <interface-number>Digital Diagnostics Monitoring (DDM), also known as Digital Optical Monitoring (DOM) or Diagnostic Monitoring Interface (DMI), is a standardized feature defined by SFF-8472 that allows network devices to monitor real-time optical transceiver parameters such as temperature, voltage, transmit power. When optical modules operate on a switch, it is usually necessary to read the module's internal information to understand its working status—such as connection status and real-time metrics like optical power and temperature. Additionally, identifying module information helps detect coding. If the same port with the same optical module has link, then I do get a proper readout of the optical monitor command (tx power / rx power / temps / current). This guide provides complete, step-by-step CLI commands to view module type, DOM/DDM diagnostic data.
[PDF Version]