Related Topics:
Scalable Network Security Automation-
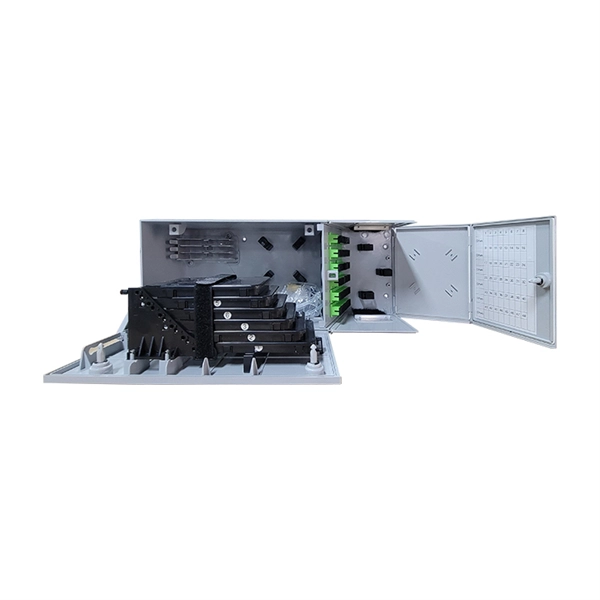
Is the DTU distribution network automation terminal a device
DTU is a terminal device of a switching station, generally installed in conventional switching station, outdoor small switching station, ring network cabinet, small substation, box-type substation, etc. DTU distribution network automation terminal is such an intelligent device, which can greatly improve the efficiency of distribution network management and reduce human errors, and provide timely and accurate monitoring and control of the power distribution system. It completes the acquisition and calculation of position signal, voltage, current, active power. Data Transfer Unit (DTU), also known as a "data transmission unit, concentrator, converter, or repeater," typically functions as a router or gateway. It supports multiple industrial protocols (e. Overview of DTU Distribution Network Automation Terminal Device: The DTU. This page is a practical guide for designing feeder automation terminals (FTU, DTU and TTU) with the right mix of sensing, communication, power, security and IC choices. It is usually deployed at various nodes of the IoT, serving as a bridge between the physical world and the digital world.
[PDF Version]
-
Office Network Security Equipment Configuration Standards
For improved network security, the Trusted Computing Group (TCG) is developing standards/guidance that specifically addresses the security of networking equipment. The TCG Guidance for Securing Network Equipment Preview Synopsis provides a summary of the ongoing. Establish, implement, and actively manage (track, report on, correct) the security configuration of network infrastructure devices using a rigorous configuration management and change control process in order to prevent attackers from exploiting vulnerable services and settings. Why is this CIS. This publication has been developed by NIST in accordance with its statutory responsibilities under the Federal Information Security Modernization Act (FISMA) of 2014, 44 U. NIST is responsible for developing information security standards and. Securing network devices is essential for preventing unauthorized access and maintaining network integrity. By enforcing standardized security policies and. This article provides best practices for each of these aspects, ensuring a robust and efficient office network setup. Steps for Provisioning Servers 3.
[PDF Version]
-
Pole-mounted switches for distribution network automation
Pole-mounted switches are essential components in 10kV overhead distribution lines, particularly in suburban and rural power networks. Scada-Mate Switches are integer style three-pole, group-operated load interrupter switches available in voltage ratings of 14. The HZW32-12/M630 series magnetic control pole-mounted circuit breaker is an outdoor distribution device with a rated voltage of 12kV and a three-phase. This is a total end-to-end solution for secondary distribution substations, comprising of 'packaged' compact substation and grid automation solution cabinet to facilitate digitalization. Their flexible designs include options for local and remote operation, as well as integration with automation and automatic transfer control solutions. Our. CYG SUNRI's independently developed New Solution of Integrating Pole-Mounted Primary Equipment and Secondary Equipment Based on Internet of Things adopts various technologies such as all-electronic sensors, capacitance extraction, and low power consumption perception terminals.
[PDF Version]
-
Use network security equipment correctly and effectively
There are 8 steps to managing your network's security including: Be Organized. Develop and enforce a strong password policy. Build a vulnerability management program. We'll explore how powerful solutions, like those from industry leaders Cisco and Meraki, can help you build secure, seamless. This guide provides a detailed roundup of the most critical network security best practices for modern enterprises.
-
Distribution Network Automation Management Center
ADMS provides distribution utilities with real-time monitoring and control, network analysis, network optimization and outage management capabilities in an integrated software architecture, enabled by a high-performance, scalable, and cybersecure SCADA platform. 50ased solutions optimizes customers' distribution networks. Solution based on Relion series and other EPMV-DA Products improve safety, reliability and efficie oducts, combining a w expansion and interoperability Installati on power calculation and Frequency load shedding as backup. Ensure an efficient, stable, secure and sustainable power supply and. Distribution automation (DA) is a family of technologies, including sensors, processors, information and communication networks, and switches, through which a utility can collect, automate, analyze, and optimize data to improve the operational efficiency of its distribution power system. Our Network Manager ADMS delivers.
[PDF Version]
-
Distribution Network Automation Deployment
Explore how high-volume distributors can use ERP deployment automation to accelerate logistics transformation, reduce rollout risk, standardize workflows, and improve warehouse, transportation, and order orchestration performance across complex distribution networks. This document offers a complete guide to Cisco's Smart Grid Field Area Network (FAN) solution architecture. High-volume distribution. Distribution automation allows utilities to detect feeder faults, isolate the damaged section, and restore service through automated switching and FLISR control logic. Distribution. Distribution networks have traditionally had low levels of automation and control, primarily centered around the use of SCADA to monitor medium voltage (MV) feeders together with a lower usage of distribution management, voltage control, and automatic reconfiguration systems. But there's a massive gap between having a working script on your laptop and deploying something that non-programmers.
[PDF Version]
-
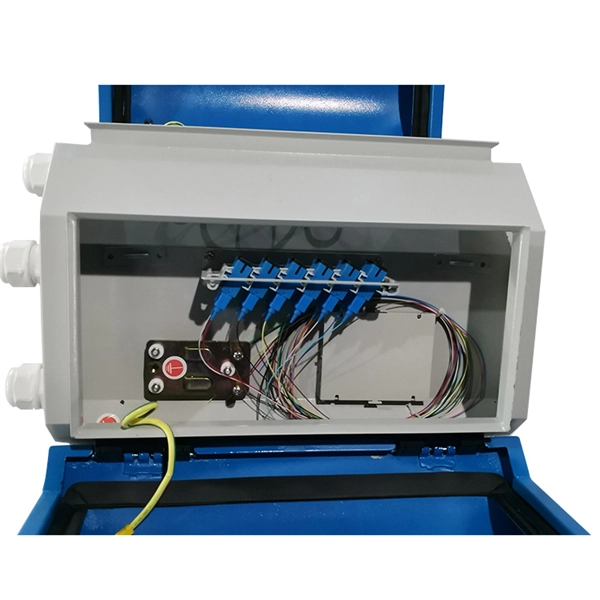
Network security device management interface
Cisco's Adaptive Security Device Manager (ASDM) is a web-based tool designed to manage network security devices from a central location. It serves as a user-friendly graphical interface for configuring, monitoring, and troubleshooting Cisco firewall appliances. Watch this demo for securing your firewall management interface, which details best practices for securing your management. The Cisco Router and Security Device Manager (SDM) is an intuitive, graphical user interface. For more information about Cisco SDM, please visit By enforcing standardized security policies and. Exposed network device management interfaces on the internet, encompassing routers, switches, and firewalls, represent critical attack vectors that demand immediate identification and stringent security measures.
[PDF Version]
-
Standard Cable Management for Network Patch Panels
Patch panel wire management involves the organized routing, securing, labeling, and maintenance of cables connected to a network patch panel. Patch panels serve as the central termination point for Ethernet, fiber, and other structured cabling systems in data centers and network. You'll learn how to design rack layouts that scale, implement labeling systems that survive staff turnover, and select the right structured cabling components for your specific environment — whether that's a 12-cabinet edge closet or a multi-megawatt AI training facility. It can be at an office, a big data center, or a simple home setup. Horizontal Cable Managers: Installed inside the cabinet, typically with. A certification tool, such as a Fluke Networks DSX CableAnalyzer, tests against TIA performance standards, measuring parameters like insertion loss and NEXT (near-end crosstalk) for the specific cable category. This process generates a pass/fail report for every cable run, guaranteeing that your. Even as Wi-Fi 6E and Wi-Fi 7 push uplink bandwidth to 5G/10G and PoE++ powers more devices than ever, the patch panel continues to play an essential role in structured cabling.
[PDF Version]
-
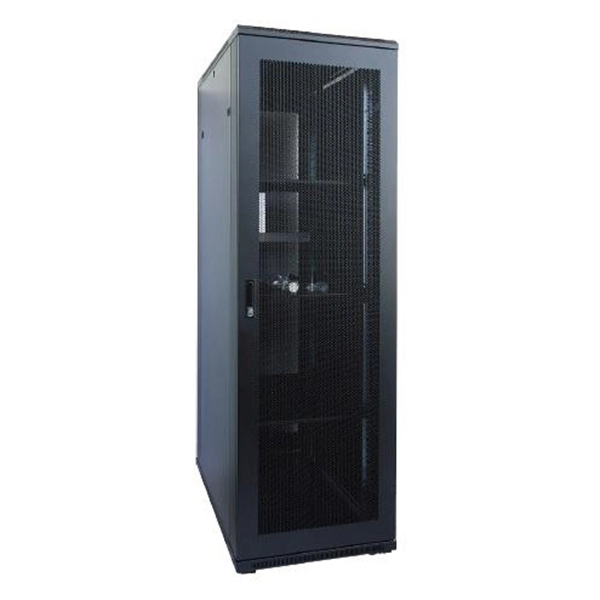
Power grid private network server rack dimensions and parameters
The three primary dimensions to consider are rack height (measured in rack units or U), rack width (most commonly the industry-standard 19-inch format), and rack depth (typically ranging from 24 inches to 48 inches). In this landscape, Dell PowerEdge rack servers stand out as a leading choice for IT professionals and data center managers looking to transform their infrastructure. Dell PowerEdge R-Series servers: A comprehensive lineup of rack servers designed to meet the rigorous demands of modern, scalable. The DellTM PowerEdgeTM rack enclosures are designed to hold and protect server, network and data storage equipment. Use the following specifications to plan for your server. We offer private server racks of up to 55U in our data centers.