Related Topics:
Vlan Routing Layer Switch-
Access Layer Switch VLAN and MAC Binding
The MAC-based VLAN feature allows incoming untagged packets to be assigned to a VLAN and in that way, you can classify traffic based on the source MAC address of the packet. You can use VLAN maps to filter traffic between devices in the same VLAN. Unsupported protocols are. VLANs can be assigned based on interfaces, MAC addresses, IP subnets, protocols, and policies (MAC addresses, IP addresses, and interfaces). Table 5-2 compares different VLAN assignment modes. A network administrator preconfigures a PVID for each interface on. In this article, we will dive into switching basics, focusing specifically on VLANs (Virtual Local Area Networks) and MAC address tables, two critical components in managing traffic within local networks. It is required that Laptop A can only access Server A and Laptop B can only access Server B, no matter which meeting room the laptops are being used in. VLAN access-map configuration is very similar to the Route-map configuration.
[PDF Version]
-
Port down after VLAN segmentation on access layer switch
Symptom: The switchport is shutting down or not passing traffic after connecting a device. Cause: Port security may be misconfigured, leading to violations that cause the port to go into an error-disabled state. Please rate and mark as an accepted solution if you have found any of the information provided useful. This then could assist others on these forums to find a valuable answer and broadens the. An SVI stuck in up/down means something is wrong with the underlying VLAN — no active ports, a deleted VLAN, or STP blocking every path. Here is how to diagnose and fix every cause. You configure an SVI, assign an IP address, type no shutdown, and expect it to come up. Instead, show ip interface. Network segmentation is crucial for security, performance, and efficient network management., computers, printers) connect to a switch.
[PDF Version]
-
Front-end access layer switch
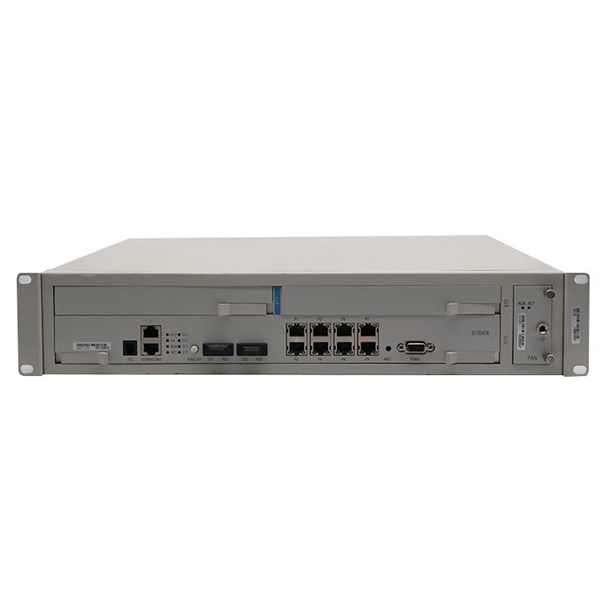
Access Layer Switches: Operating at the network's edge, access switches connect end-user devices like PCs, printers, IP phones, and wireless access points. They are characterized by high port density, cost-effectiveness, security features at the edge, and often PoE support. The access layer is where endpoints (such as phones, laptops, video-conferencing sets, printers, IoT sensors, IP cameras, and servers) are primarily connecting to the network. Wireless access points are also connected here and provide further access.
-
Configure a Layer 3 Core Switch
To start using layer 3 routing, navigate to the Switching > Configure > Routing & DHCP page. You can configure a port as a Layer 2 interface or a Layer 3 interface. A routed interface is a physical port that. UPDATED: 2020 – Cisco Catalyst switches equipped with the Enhanced Multilayer Image (EMI) can work as Layer 3 devices with full routing capabilities. On a Layer3-capable switch, the port interfaces work as. This article outlines a basic example of how layer 3 routing functionality on MS series switches could be implemented. Sign in with your Cisco SSO or create a free account to start. Layer 3 interfaces are used to forward IPv4 and IPv6 packets using static or dynamic routing protocols. This example uses router configurations of AR3600 V200R007C00SPCc00.
[PDF Version]
-
Access Switch VLAN ID
Creates an access interface and assigns an VLAN ID to it. VLANs can only be assigned to non-routed (Layer 2) interfaces. Use routing and no routing commands to move ports. This article provides instructions on how to configure an interface VLAN as an access or trunk port on your switch through the Command Line Interface (CLI). Virtual LAN (VLAN) implementation is recommended in ESXi networking environments because: There are three methods of VLAN tagging that can be configured on ESXi: All VLAN tagging of packets is performed on the physical switch. Let me give you the most important rule, the rule that should not be broken – 1 VLAN equals 1 subnet.
-
What layer switch is the core switch
A core switch is a high-capacity, high-performance Layer 3 switch positioned at the physical backbone of an enterprise network. The primary transmission and routing of data signals take place at the core layer only. The devices like high-capacity transmitters are placed in this. A core switch is the backbone of a large-scale network, designed to handle massive volumes of traffic with ultra-low latency and maximum reliability. Usually, complex network systems at the offices and data centers utilize the core switch to divide the traffic. In these switches, the data routed and switched.
-
Aggregation Layer Switch 5130
The HPE FlexNetwork 5130 EI is a Layer 2—LAN switching device designed for high-performance networking. This device is capable of delivering maximum efficiency with features such as link aggregation, spanning tree protocol, and VLANs. This includes: For more information, see pages 177, 188, 194, 200, 204, 209, 212 and 216 of the manual. Was this helpful? How do I. Below you will find brief information for Ethernet switch 5130 EI Switch. Major advantage: double the speed and the redundancy Works on most of HPE Switches 5130, 5140, 5510, etc. HP 5130 EI Switch Series comprises Gigabit Ethernet switches that support static and RIP Layer 3 routing, diversified services, and IPv6 forwarding, as well as provides four 10-Gigabit Ethernet (10GbE) extended interfaces. Unique Intelligent Resilient Framework (IRF) technology creates a virtual.
[PDF Version]
-
Cisco Access Layer Switch Permissions
Cisco IOS devices use privilege levels for more granular security and Role-Based Access Control (RBAC) in addition to usernames and passwords. To access Cisco Feature Navigator, go to http://www. By default: Each command in IOS is assigned a default. We can configure different command access based on priviledge level of user logged in. Level 15. In this guide, we'll break down everything you need to know about Cisco ACLs: from the basics of standard and extended lists, to advanced configuration examples, to real-world troubleshooting tips that save hours of downtime. If the startup configuration has a convoluted type 9 secret, and you downgrade to a release prior to Cisco IOS XE Gibraltar 16. 2, you can/may be locked out of the device.
-
Configure the access route for the Layer 3 switch
To start using layer 3 routing, navigate to the Switching > Configure > Routing & DHCP page. Under L3 routing tab, click Configure - which takes you to. Layer 3 interfaces forward packets to another device using static or dynamic routing protocols. You can configure a port as a Layer 2 interface or a Layer 3 interface. That is, you can assign an IP address directly on the routed port. First, create the two VLANs as shown in Example 4-13.
-
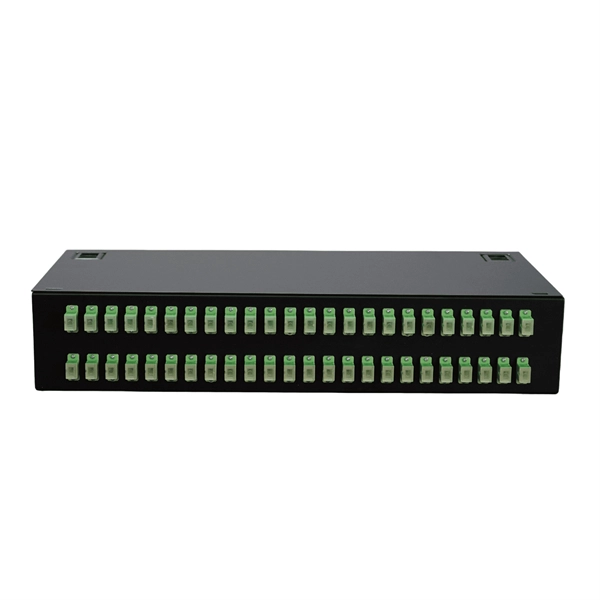
Huawei Network Switch Optical Port Configuration
To enable a port on a Huawei switch, start by accessing the device's command-line interface (CLI) via a console cable or SSH. Use the system-view command to enter configuration mode, then navigate to the target port using interface GigabitEthernet 0/0/1 (replace. This section describes how to configure attributes for an optical interface. The interface split function allows a high-bandwidth physical interface on the device to be configured as multiple independent low-bandwidth interfaces. Whether you're setting up a new network segment or troubleshooting connectivity issues, understanding how to enable ports properly ensures seamless data flow while maintaining security. Single-mode/multimode fibers and. Do you have a question about the OptiX OSN 7500 and is the answer not in the manual? Page 1 HUAWEI OptiX OSN 7500 Intelligent Optical Switching System Technical Manual System Description V100R001 Huawei Technologies Proprietary. Enabling Telnet Service and Granting Access on.
[PDF Version]
-
Which layer device is typically used in an access switch
Access switches are layer 2 switches that operate at OSI model layer 2 (data link layer). It typically sits at the access layer, provides high port density, often delivers PoE, and forwards traffic. The access layer plays a critical role in connecting end devices—such as computers, printers, IP phones, and wireless access points—to the rest of the enterprise network. This guide will demystify these roles and help you understand their. The core switch is a high-end device that is used to connect all the access switches. The access layer is supposed to make it easier for end devices to stay connected.
-
Fiber optic leased line connected to a Layer 3 switch
A leased line is not a long physical cable extended to two or more locations as others perceived. It uses a specialized switching device that acts as a signal booster to make the connection a point-to-point li.